Credential theft is now at an all-time high and is responsible for more data breaches than any other type of attack.
With data and business processes now largely cloud-based, a user’s password is the quickest and easiest way to conduct many different types of dangerous activities.
Being logged in as a user (especially if they have admin privileges) can allow a criminal to send out phishing emails from your company account to your staff and customers. The hacker can also infect your cloud data with ransomware and demand thousands of dollars to give it back.
How do you protect your online accounts, data and business operations? One of the best ways is with multi-factor authentication (MFA).
It provides a significant barrier to cybercriminals even if they have a legitimate user credential to log in. This is because they most likely will not have access to the device that receives the MFA code required to complete the authentication process.
WHAT ARE THE THREE MAIN METHODS OF MFA?
When you implement multi-factor authentication at your business, it’s important to compare the three main methods of MFA and not just assume all methods are the same. There are key differences that make some more secure than others and some more convenient.
Let’s take a look at what these three methods are:
SMS-BASED
The form of MFA that people are most familiar with is SMS-based. This one uses text messaging to authenticate the user.
The user will typically enter their mobile number when setting up MFA. Whenever they log into their account, they will receive a text message with a time-sensitive code that must be entered.
ON-DEVICE PROMPT IN AN APP
Another type of multi-factor authentication will use a special app to push through the code. The user still generates the MFA code at login. Rather than receiving the code via SMS, it’s received through the app.
This is usually done via a push notification and it can be used with a mobile app or desktop app in many cases.
SECURITY KEY
The third key method of MFA involves using a separate security key that you can insert into a PC or mobile device to authenticate the login. The key itself is purchased at the time the MFA solution is set up and will be the thing that receives the authentication code and implements it automatically.
The MFA security key is typically smaller than a traditional thumb drive and must be carried by the user to authenticate when they log into a system.
Now, let’s look at the differences between these three methods.
MOST CONVENIENT FORM OF MFA?
Users can often feel that MFA is slowing them down. This can be worse if they need to learn a new app or try to remember a tiny security key. What if they lose that key?
This user inconvenience can cause companies to leave their cloud accounts less protected by not using multi-factor authentication.
If you face user pushback and are looking for the most convenient form of MFA, it would be the SMS-based MFA.
Most people are already used to getting text messages on their phones so there is no new interface to learn and no app to install.
MOST SECURE FORM OF MFA?
If your company handles sensitive data in a cloud platform, such as your online accounting solution, then it may be in your best interest to go for security.
The most secure form of MFA is the security key.
The security key, being a separate device altogether, won’t leave your accounts unprotected in the event of a mobile phone being lost or stolen. Both the SMS-based and app-based versions would leave your accounts at risk in this scenario.
The SMS-based is actually the least secure because there is malware out there now that can clone a SIM card which would allow a hacker to get those MFA text messages.
A Google study looked at the effectiveness of these three methods of MFA at blocking three different types of attacks. The security key was the most secure overall.
Percentage of attacks blocked:
- SMS-based: between 76 - 100%
- On-device app prompt: between 90 - 100%
- Security key: 100% for all three attack types
WHAT IS IN BETWEEN?
So, where does the app with an on-device prompt fit in? Right in between the other two MFA methods.
Using an MFA application that delivers the code via push notification is more secure than the SMS-based MFA. It’s also more convenient than needing to carry around a separate security key that could quickly become lost or misplaced.
LOOKING FOR HELP SETTING UP MFA AT YOUR COMPANY?
Multi-factor authentication is a “must-have” solution in today’s threat climate. We would be happy to discuss your barrier points and come up with a solution together to keep your cloud environment better secured.
You can reach us at (860) 577-8060 or via our contact form.
We have seen some of the greatest and most troubling cyberattacks since the birth of the Internet age in the last few years. These hacks appear to be leaning toward larger firms and organizations and include the intrusion on Sony's PlayStation that claimed the personal information of over 25 million people to the largest password breach ever of 8.4 billion passwords. Read more
Having your laptop stolen is unpleasant because you need to replace an expensive piece of hardware which risks your digital security. Fortunately, you can take precautions before and after your laptop goes missing.Read more
Stolen login credentials are a hot commodity on the Dark Web. There are prices every type of online account from banking to social media. For example, hacked social media accounts will go for between $30 to $80 each.
The rise in reliance on cloud services has caused a big increase in breached cloud accounts. Compromised login credentials are now the #1 cause of data breaches globally according to IBM Security’s latest Cost of a Data Breach Report.
Having either a personal or business online account compromised can be very costly. It can lead to a ransomware infection, compliance breach, identity theft and more.
To make matters more challenging, users are still adopting bad password habits that make it all too easy for criminals. For example:
- 34% of people admit to sharing passwords with colleagues
- 44% of people reuse passwords across work and personal accounts
- 49% of people store passwords in unprotected plain text documents
Cloud accounts are more at risk of a breach than ever. However, there are several things you can do to reduce the chance of having your online accounts compromised.
USE MULTI-FACTOR AUTHENTICATION (MFA)
Multi-factor authentication (MFA) is the best method there is to protect cloud accounts. It is not a failsafe but it is proven to prevent approximately 99.9% of fraudulent sign-in attempts according to a study cited by Microsoft.
When you add the second requirement to a login, which is generally to input a code that is sent to your phone, you significantly increase account security. In most cases, a hacker is not going to have access to your phone or another device that receives the MFA code and thus they won’t be able to get past this step.
The brief inconvenience of using that additional step when you log into your accounts is more than worth it for the bump in security.
USE A PASSWORD MANAGER FOR SECURE STORAGE
One way that criminals get their hands on user passwords easily is when users store them in unsecured ways. This includes an unprotected Word or Excel document or the contact application on their PC or phone.
Using a password manager provides you with a convenient place to store all your passwords and is also encrypted and secured. You only need to remember one strong master password to access all the others.
Password managers can also autofill all your passwords in many different types of browsers which makes it a convenient way to access your passwords securely across devices.
REVIEW/ADJUST PRIVACY & SECURITY SETTINGS
Have you taken time to look at the security settings in your cloud tools? One of the common causes of cloud account breaches is misconfiguration. This is when security settings are not properly set to protect an account.
You don’t want to just leave SaaS security settings at defaults because these may not be protective enough. Review and adjust cloud application security settings to ensure that your account is properly safeguarded.
USE LEAKED PASSWORD ALERTS IN YOUR BROWSER
You can have impeccable password security on your end and still have your passwords compromised. This can happen when a retailer or cloud service that you use has their master database of usernames and passwords exposed and the data stolen.
When this happens, those leaked passwords can quickly end up for sale on the Dark Web without you even knowing it.
Due to this being such a prevalent problem, browsers like Chrome and Edge have had leaked password alert capabilities added. Any passwords that you save in the browser will be monitored and you will see an alert when you use it if it is found to be leaked.
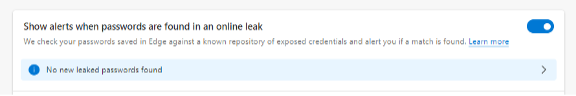
Look for this in the password area of your browser because you may need to enable it. This can help you know as soon as possible about a leaked password so that you can change it.
DON’T ENTER PASSWORDS WHEN ON A PUBLIC WI-FI
Whenever you’re on public Wi-Fi, you should assume that your traffic is being monitored. Hackers like to hang out on public hot spots in airports, restaurants, coffee shops and other places so they can gather sensitive data like login passwords.
You should never enter a password, credit card number or other sensitive information when you are connected to public Wi-Fi. You should either switch off Wi-Fi and use your phone’s wireless carrier connection or use a virtual private network (VPN) app that encrypts the connection.
USE GOOD DEVICE SECURITY
If an attacker manages to breach your device using malware, they can often breach your online account without a password needed. Just think about how many apps on your devices you can open and already be logged in to.
To prevent an online account breach that happens through one of your devices, make sure you have strong device security. Best practices include:
- Antivirus/anti-malware
- Up-to-date software and OS
- Phishing protection (like email filtering and DNS filtering)
LOOKING FOR PASSWORD & ONLINE ACCOUNT SECURITY SOLUTIONS?
Don’t leave your online account at risk. We can help you review your current cloud account security and provide helpful recommendations.
Reach out to us at (860) 577-8060 or contact us at info@soundcomputers.net.
You can read more about about cloud accounts here.
How do you secure your company network when your employees work remotely and the rest of your team is transitioning to remote work? The days of cramped desks across a crowded office building are over for many businesses.Read more
Companies had to deal with more than just COVID complications last year as they faced brutal cyber-attacks. In fact, a new type of phishing attack was discovered after the furniture giant IKEA noticed several malicious reply-chain emails making rounds in the company. While IKEA was able to protect itself against the attack, many companies are still unaware of the lurking danger.
What Is Reply-Chain Phishing?
Reply-chain phishing is a method hackers use to put themselves into legitimate conversations by taking advantage of compromised accounts.
Unlike spear-phishing where they use fake emails similar to authentic ones, reply-chain phishing involves gaining control of a legitimate email account and using that to carry out their nefarious attack.
They obtain these legitimate emails through different methods. Once they have control of an employee’s email account, they scan through email threads looking for those with the highest chance of landing a victim. After identifying an email thread, they send an email with a malicious link attached as a reply to the thread.
Once a recipient clicks on the URL, they will unintentionally download malware that will spread through the network. Another tactic is to insert malicious links in out-of-office replies. Both tactics are a way to spread malware.
The actual owner of the email account doesn't see the reply in the email chain which means that a reply-chain attack can go unnoticed for some time.
Reply-chain phishing attacks are hard for employees to notice and react/report. This is because the emails look like they’re from a colleague when it is in fact from a colleague's account.
How Do Reply-Chain Attacks Work?
It starts with hackers taking over an email account through techniques like password-spraying, credentials stuffing or credentials dumping. They may even be using an already compromised account. After gaining access to one or more accounts, they monitor email threads for a chance to send malware or compromised links to participants in the email chain.
Reply-chain phishing is very effective since the email parties already trust each other. The hackers do not insert themselves as new participants in the ongoing conversation and they are not trying to spoof another employee's email account. Instead, they operate from behind a genuine account.
Since the attacker has access to the full thread, they can customize their nefarious message to fit the topic of an ongoing conversation. This, on top of the fact that the recipient likely trusts the sender, massively increases the chance of the victim opening the malicious attachment or clicking a dangerous link.
To simplify it all, let's say "Taylor's" account was compromised and the attacker sees that Taylor and Bethanie (and a few other team members) have been discussing a new project campaign. The attacker can take advantage of this conversation to send Bethanie a malicious link to a document/article that appears related to the conversation.
How To Protect Your Business Against Reply-Chain Hacking
There are a couple of ways to protect your company against email chain attacks. They include:
- Make sure that all employees follow best security practices with their email accounts. This includes using multi-factor authentication and setting a secure password.
- Inspect inbox and email settings regularly. Check for rules meant to filter replies to a different inbox and particularly those that weren't set by the user. If you notice any, immediately contact your IT team.
- If possible, disable all Microsoft Office Macros. Microsoft Office Macros allow users to personalize manual and automatic email replies. Unfortunately, they are a common vehicle for email attacks.
- Schedule comprehensive training sessions to increase employee awareness and knowledge about cybercrime as well as their responsibility to protect the company.
If an employee notices a reply-chain attack in progress, they should take the following steps:
- Immediately delete the email from every folder (including inbox, spam and trash).
- Reach out to other members of the email chain through a new email thread or another communication means to inform them of the attack and ask them to delete the thread from their email.
- Don't open any other message from the compromised account until the attack has been dealt with.
- Inform your security or managed IT team so they can investigate and make sure the hackers didn't compromise your systems and data.
Conclusion
With a month and a half left in Q2 2022, it's important to start beefing up your cybersecurity. This includes informing your employees about the latest methods of attack, carrying out cybersecurity awareness training, arming your IT team and creating an effective strategy to protect your data from such attacks. If it could work on a large corporation like IKEA, imagine how effective it will be on a small-scale business.
If you need additional support, Sound Computers has your business covered. Reach us on our contact form or call us at (860) 577-8060.
Cyber security training is growing in importance. Imagine if your company was compromised and every employee's financial and personal data was leaked. Can you imagine the consequences? Will your clients or stakeholders still have confidence in your business if that happens?Read more
Last year, the REvil cybercrime gang ruined the Independence Day Holiday for hundreds of American businesses after successfully launching a ransomware attack. The attack forced hundreds of companies to close temporarily. REvil demanded a ransom of $70 million to unlock their files. Read more
Social engineering refers to a broad spectrum of cyber attacks in which a malicious actor uses psychological manipulation to trick people into sharing sensitive details or clicking on a malicious link. Read more
The mobile workforce has come into its own over the last 18 months. After COVID-19 forced organizations to rethink their workplace operations, remote and mobile working quickly became a part of day-to-day business. It’s a trend that is set to skyrocket in the coming years. The International Data Corporation (IDC) believes that by 2024, 60% of the US workforce will be considered mobile workers. Read more